The Same Class of Sandbox Flaw: Cursor and OpenAI Fixed It in About a Week, Anthropic Took Roughly 50 Days and About 30 Releases
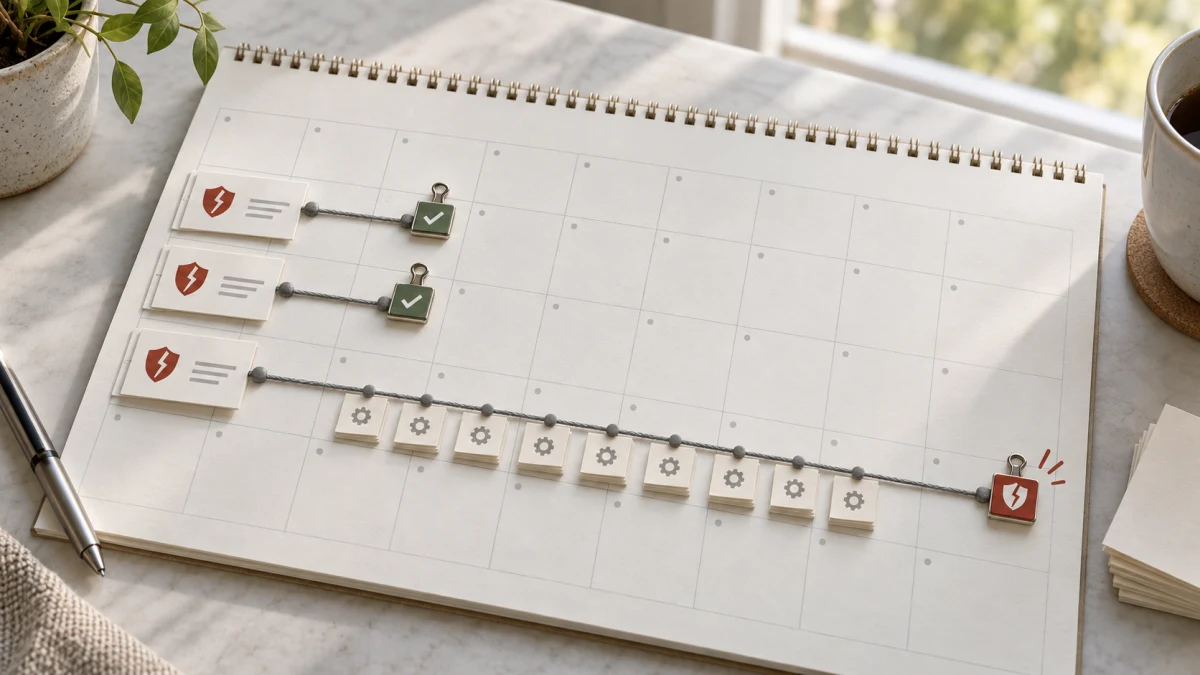
Accomplish, a security startup still in stealth (founded by Or Hiltch, Amit Avner and Guy Zipori), publicly disclosed leaky-sandbox problems in Claude Code, OpenAI Codex and Cursor after privately notifying the vendors over the summer. The newsworthy part is not the vulnerabilities but the difference in patch cadence: one flaw reported to Cursor in July and two reported to OpenAI were all fixed in roughly a week, while a similar issue reported to Anthropic about two months earlier went unpatched for some 50 days, during which the product shipped around 30 updates. Accomplish CEO Amit Avner argues attackers could have been exploiting the gaps during that window — his assessment, with no evidence of actual exploitation given in the reporting. The founders describe this as a "long tail" of lesser-known, almost normalized vulnerabilities that startups and researchers keep surfacing. In the same window, Manifold Security, Pillar Security and Cymulate each disclosed trust-boundary problems of a similar nature in coding agents.